The field notes
AI security, SOC 2, HIPAA, and the cloud-cost & scaling decisions behind real exits - written for founders and engineering leaders.
 AI Strategy
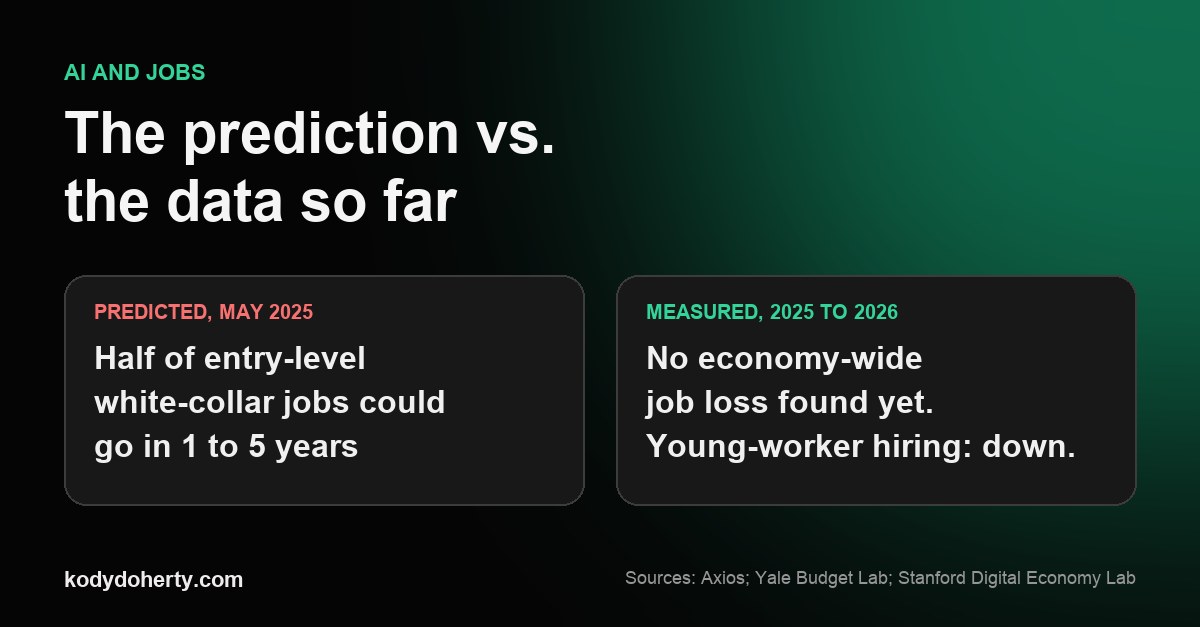
The AI Layoff Panic, Checked Against the Data
Big tech keeps predicting mass white-collar job loss. Four years after ChatGPT, here is what the controlled studies and employment data actually show, including the one signal that is real.
 AI Strategy
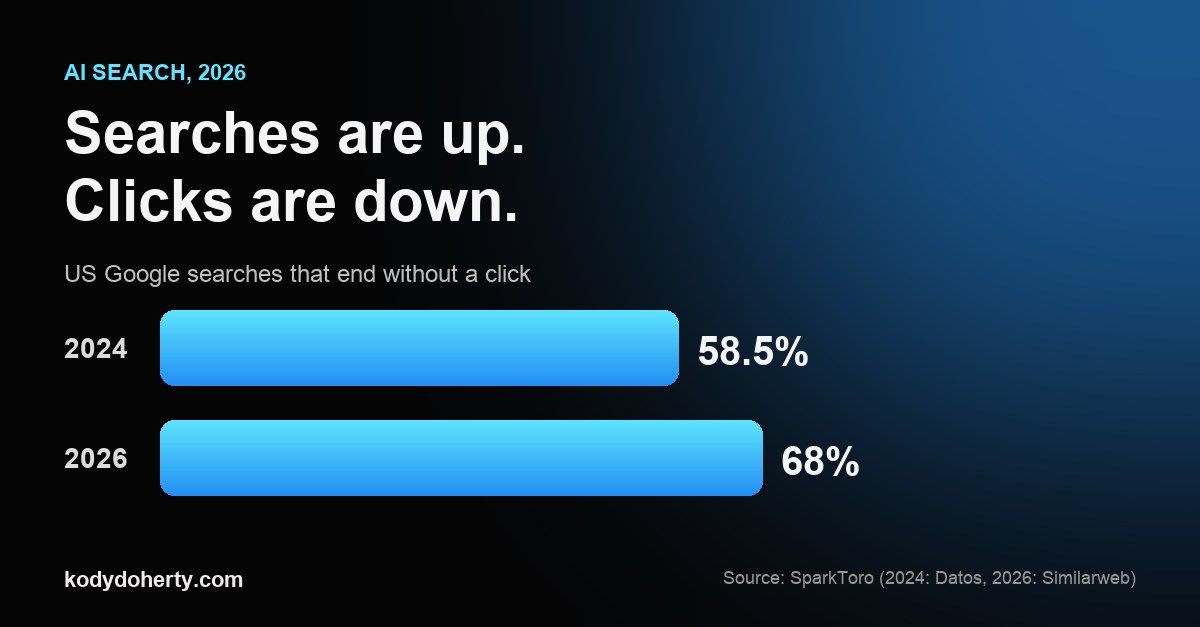
Is SEO Dead? What the 2026 Data Says About AI Search
Google searches are at record highs, but each search sends far fewer clicks. What the data from Ahrefs, Seer, Pew, SparkToro and Similarweb says about AI answer engines, and what to do about it.
 Ventures
SmileShape: SOC 2, HIPAA & an 8-Figure Valuation in Under a Year
As CTO and equity owner of SmileShape.ai, I took a health-tech AI company from day one to SOC 2 and HIPAA compliant, production-ready, and an 8-figure valuation in less than a year.
 Ventures
Pastel Protein: Launching a Product After 2 Years of R&D
Pastel Protein launches after two years of R&D. As an equity owner, here's what building a consumer product from the ground up taught me about patience, quality, and shipping.
 Ventures
Launching PracticeRank: AEO & SEO Automation for Practices
How I launched PracticeRank.ai - building the full platform that gets dental practices, medical offices, and law firms found in Google and in AI answers like ChatGPT, Perplexity, and Claude.
 Cloud & Scale
How I Cut AWS Costs 70% for a DoD Contractor
A real case study: the architecture fixes, right-sizing, and governance changes that took a defense contractor's AWS bill down 70% - without a migration or a re-platform.
 Cloud & Scale
Scaling from Zero to $50M: The Infrastructure Decisions That Mattered
A case-study reflection on the architecture, hiring, and cost decisions that actually mattered scaling a startup from zero to $50M - and the ones that didn't.
 AI Security
 for Startups: A Practical Threat Model
A founder-friendly AI security threat model: what changes when you ship LLM features, the real attack surface, and where to start protecting your product.
 SOC 2
SOC 2 for Seed-Stage Startups: What It Actually Takes
A founder's guide to SOC 2 for seed-stage startups: what it is, the 5 Trust Services Criteria, the real process and timeline, and how to avoid over-scoping.
 HIPAA
HIPAA Compliance for Health Tech Startups: A Builder's Guide
What HIPAA actually requires of a software company: PHI, the Security Rule's safeguards, BAAs, and a builder's checklist to get compliant without over-engineering.
 AI Security
Securing LLM Apps: Prompt Injection, Data Leakage & Guardrails
A practical deep dive on the top three LLM security risks - prompt injection, data leakage, and weak guardrails - with concrete mitigations you can ship this week.
 AI Security
Should You Let AI Agents Touch Production? A CTO's Framework
A CTO's decision framework for giving AI agents write access to production: blast radius, reversibility, permission scoping, sandboxing, audit logs, and kill switches.
 SOC 2
SOC 2 Type I vs Type II: Which Do You Need (and When)?
SOC 2 Type I vs Type II explained: point-in-time vs over-a-period, when each makes sense, how to sequence them, and what enterprise buyers actually accept.
 SOC 2
SOC 2 on AWS: The Controls That Actually Matter
A practical mapping of SOC 2 controls to AWS: IAM, CloudTrail/Config logging, encryption, backups, change management, vuln scanning, and access reviews.
 HIPAA
HIPAA on AWS: BAAs, Encryption, and the Config That Passes Audit
The practical AWS setup for HIPAA: the AWS BAA, HIPAA-eligible services, KMS encryption, access controls, and audit logging that actually stands up to review.